yahoo Press
JPMorgan, Visa, and Mastercard disclose cyberattack on third-party vendors
Images
1 / 6

2 / 6

3 / 6
4 / 6
5 / 6
6 / 6
The above button links to Coinbase. Yahoo Finance is not a broker-dealer or investment adviser and does not offer securities or cryptocurrencies for sale or facilitate trading. Coinbase pays us for certain activity generated through this link. Prices displayed are informational.

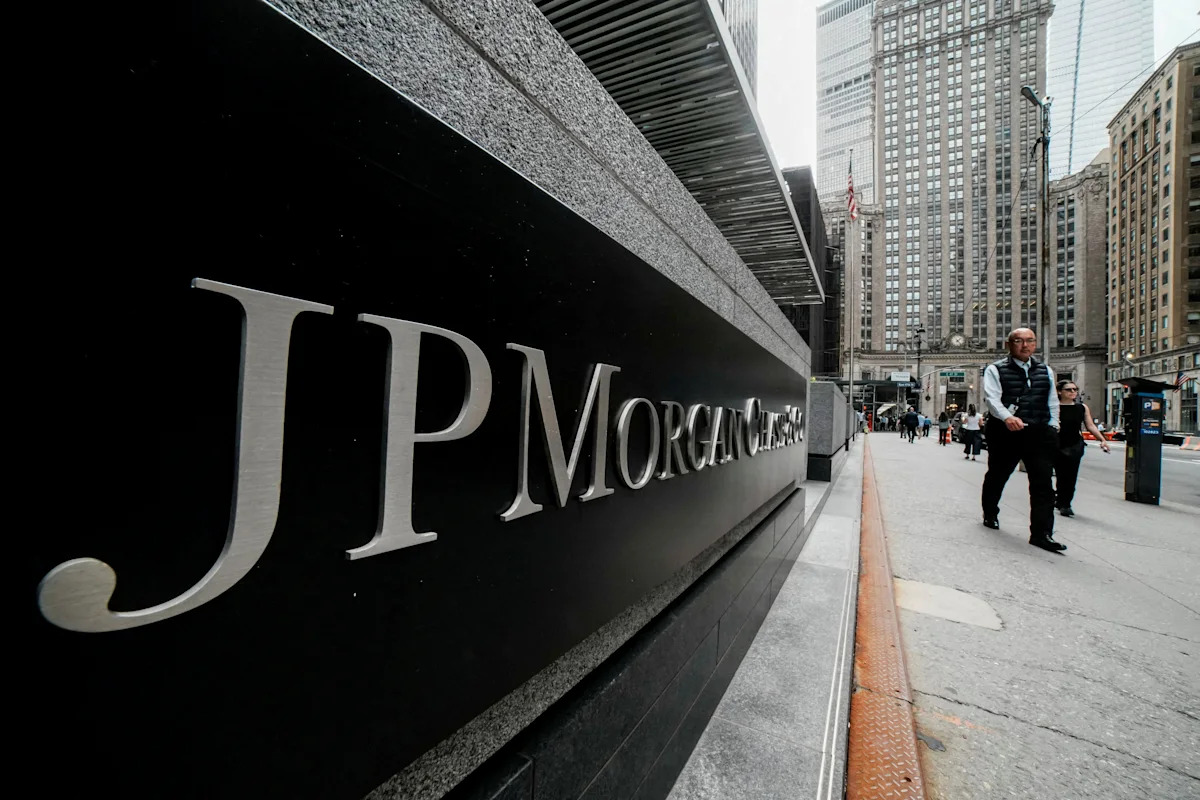
JPMorgan Chase (JPM), Visa (V), and Mastercard (MA) said on Thursday that some select customer data, including names and emails, was accessed by attackers after a cyberattack on a vendor.

Spokespeople for the companies said no payments or card data was leaked and that their own systems were not affected by the incident.

JPMorgan said it believes hackers who attacked a third-party vendor accessed marketing data, including customer names and email addresses. The bank also said the incident isn't related to outages many of its customers reported earlier this week, which it blamed on a software bug.

"Based on our investigation so far, we believe the attackers accessed certain marketing data held by those vendors, which may include some customer names and email addresses," a JPMorgan spokesperson said.

"We were recently informed of an incident at a third-party provider that resulted in the exposure of limited amount of email addresses – non-payments information – from a small subset of cardholders enrolled in a specific benefit program," a Mastercard spokesperson said. "There is no impact to the Mastercard payment network or the ability for people to use their cards," the person added.

A Visa spokesperson added claims of the incident are associated to a third-party service provider in the Asia Pacific region.

"This is unrelated to any of the system disruptions across different industries this past week," the Visa spokesperson added.

A ransomware group known as n0n has claimed responsibility for the attacks on the dark web and shared sample data as proof, according to cybersecurity firm SOCRadar.

The cybersecurity firm told Yahoo Finance that it hasn't independently verified whether the ransomware group carried out the intrusion. It also supported JPMorgan, Visa and Mastercard's statements that the breaches most likely originated at a third-party vendor and involved marketing and benefit-program data such as names and email addresses.

"The most immediate risk for consumers is targeted phishing that impersonates their bank or card provider," SOCRadar chief information security officer Ensar Seker said in an emailed statement.

The latest incident comes as consumers are on high alert after a string of major technology outages this November. The Wall Street Journal earlier reported the connection between the breaches and the ransomware group.

Follow David Hollerith on X @DsHollers.

Follow Brooke DiPalma on X at @BrookeDiPalma or email her at bdipalma@yahoofinance.com.
Comments
You must be logged in to comment.